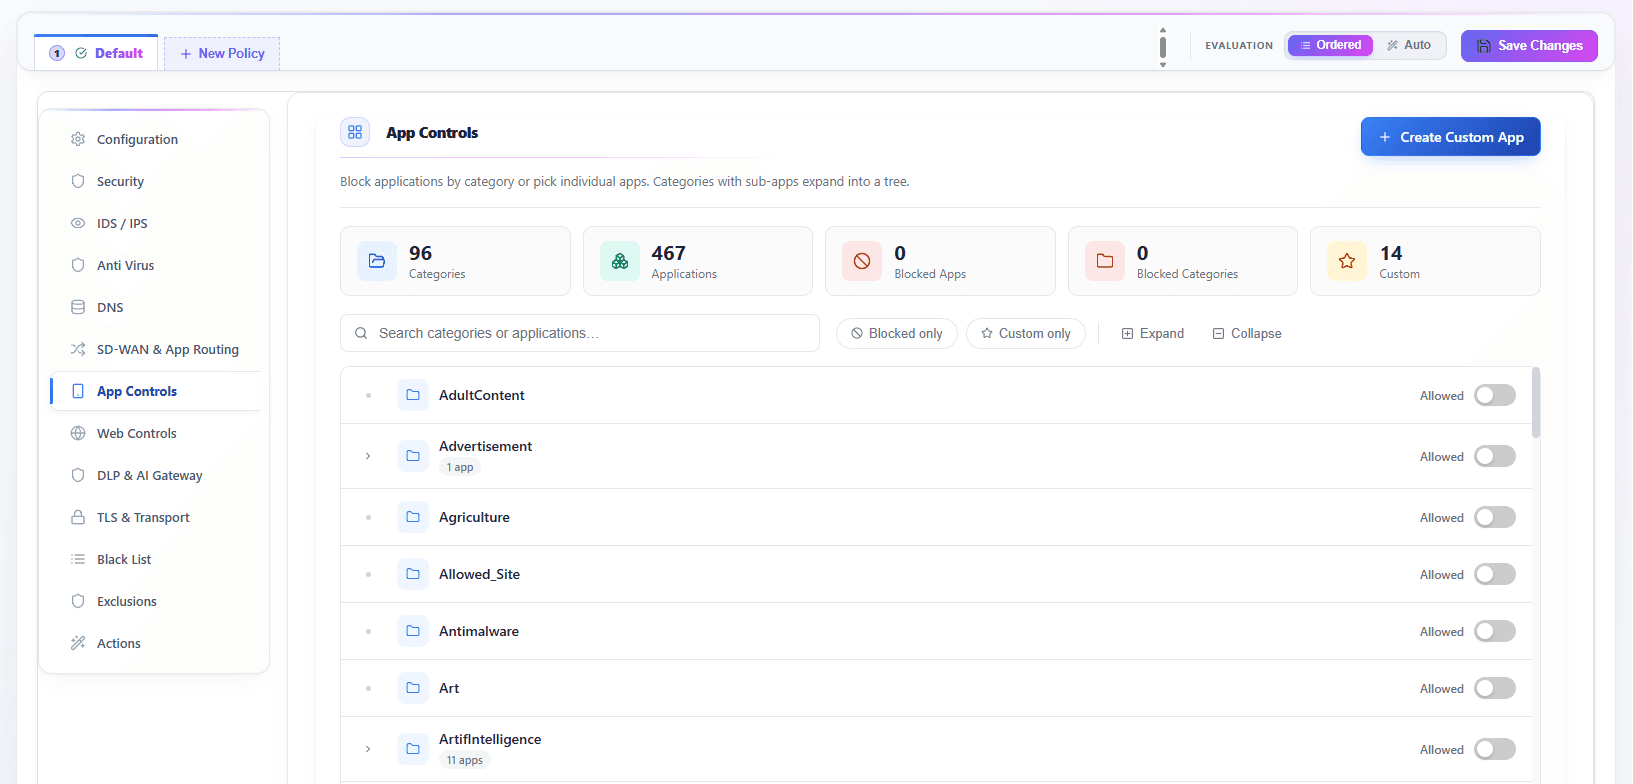
Recognises applications, not ports200+
Almost everything is HTTPS on 443, so a port-based rule can only permit or deny all of it.
OPNsense Eklentisi
Bir paket deposundan kurulur ve Servisler altında görünür. Ekibinizin zaten kullandığı arayüzün içinde dokuz sayfa — pano, cihazlar, canlı oturumlar, raporlar, politikalar, ayarlar, bildirimler, güncelleme ve destek.
The firewall you run today decides by address and port. Zedmos installs into it and decides by what the traffic actually is, who it belongs to, and what it is carrying — without replacing anything that already works.
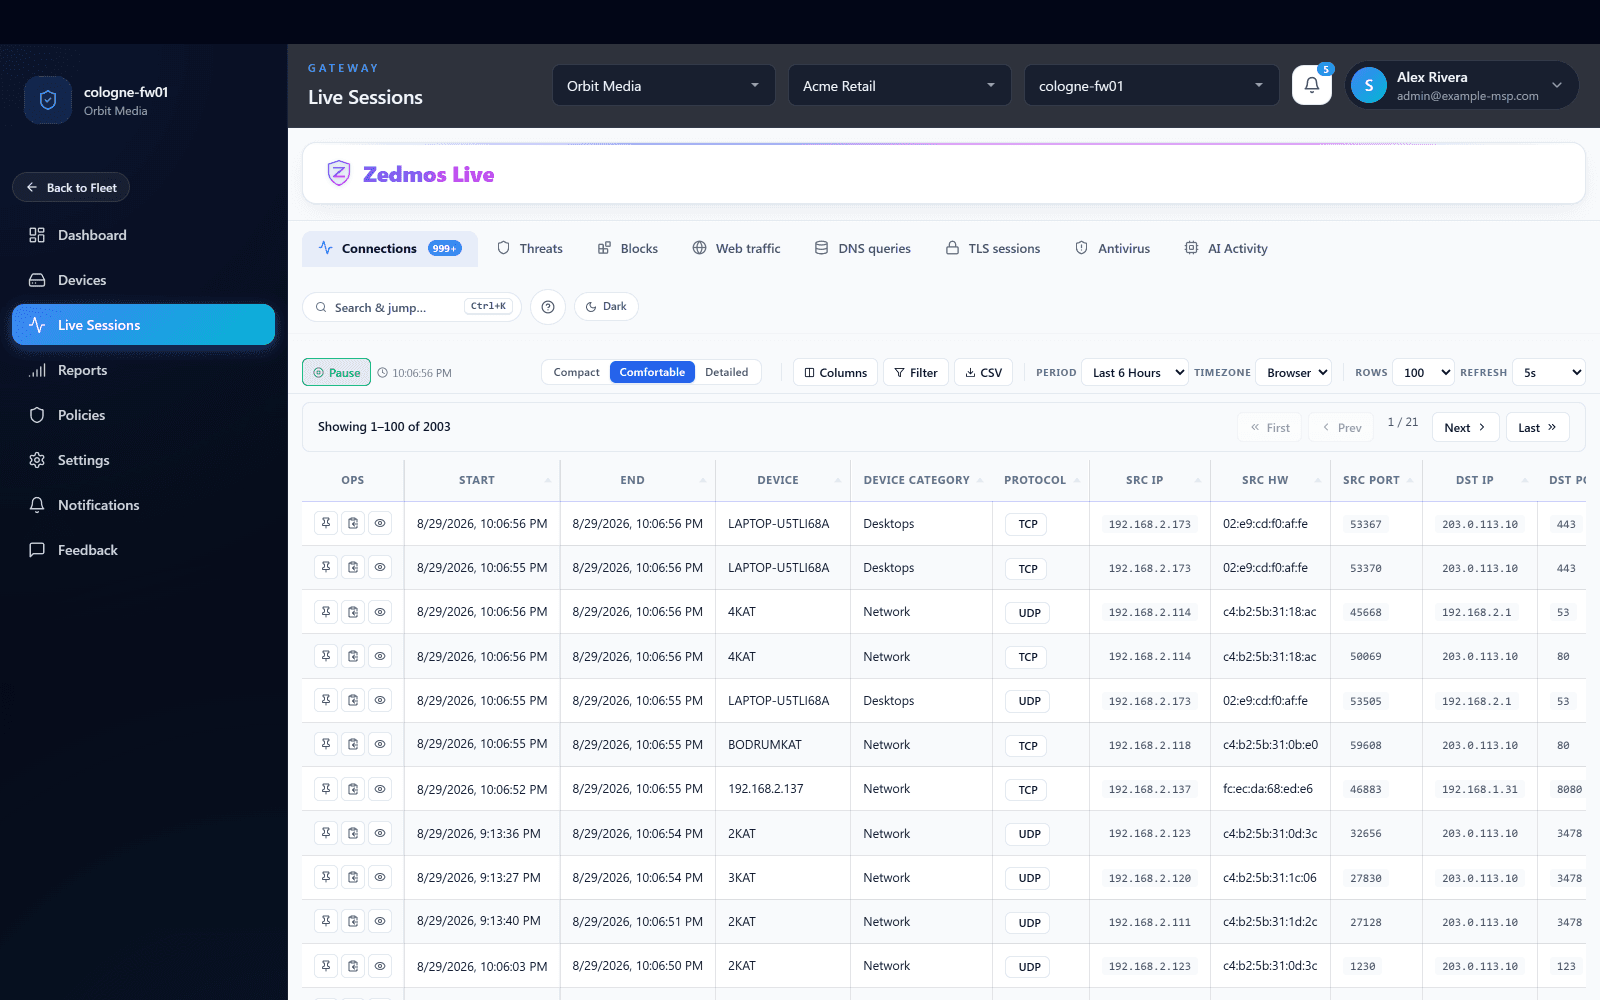
Her akış, porta göre değil uygulamaya göre sınıflandırılmış — bağlantılar sekmesi, diğer her şeyin ham maddesidir.
Cihaz, kategorisi ve donanım adresi akışla aynı satırda; böylece bir politika bir adres yerine bir kişiyi ya da grubu adlandırabilir.
Aynı güvenlik duvarı için tehditler, engellemeler ve virüs bulguları bir sekme uzakta — imzalar ve istihbarat, oturum iletilmeden önce uygulandı.
TLS oturumları ve yapay zekâ etkinliği: hangi hizmetlerin, kimler tarafından kullanıldığı ve içerik incelemesinin gönderilende ne bulduğu.
Müşteri, şube ve güvenlik duvarı en üstten seçilir. Aynı görünüm, hangi platformu çalıştırırsa çalıştırsın filodaki her güvenlik duvarı için vardır.
Grouped by the question each one answers. The same set on OPNsense, on pfSense and on Zedmos NGFW — one engine, one policy model, three ways to run it. Each has a fuller technical write-up under Resources.
Almost everything is HTTPS on 443, so a port-based rule can only permit or deny all of it.
Bump what you choose to; leave banking and health traffic alone by rule.
JA3, JA4 and ALPN identify the software behind a session even when it is not decrypted.
The protocol most of the web moved to, seen and controlled rather than left as a gap.
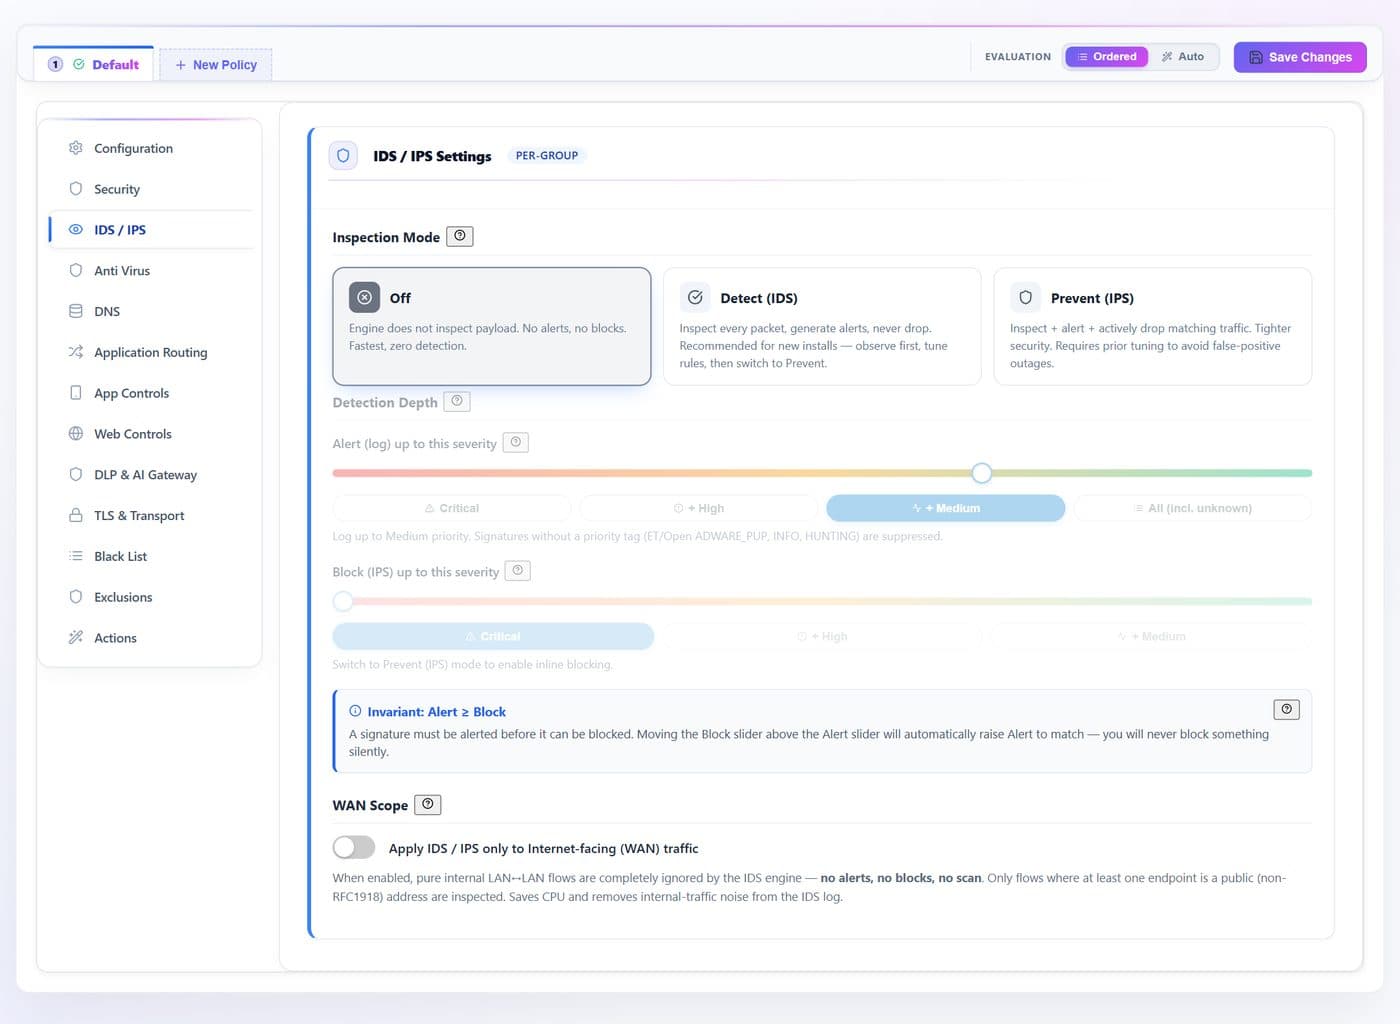
Encrypted resolution routes around a classic firewall's name-based rules. Not around this one.
Every flow on screen as it happens, carrying the decision and what drove it.
Signatures evaluated inline on the same appliance — a match is a block, not a morning alert.
Indicators gathered and cross-checked, then pushed to every firewall you manage.
Attachments and downloads examined before they land, not after.
Allow, log, rate-limit, quarantine, reset, drop — and the rest, on both platforms.
Which assistants are in use and by whom — answered without reading a single prompt.
Source code, credentials and regulated data caught on the way out, not in a breach report.
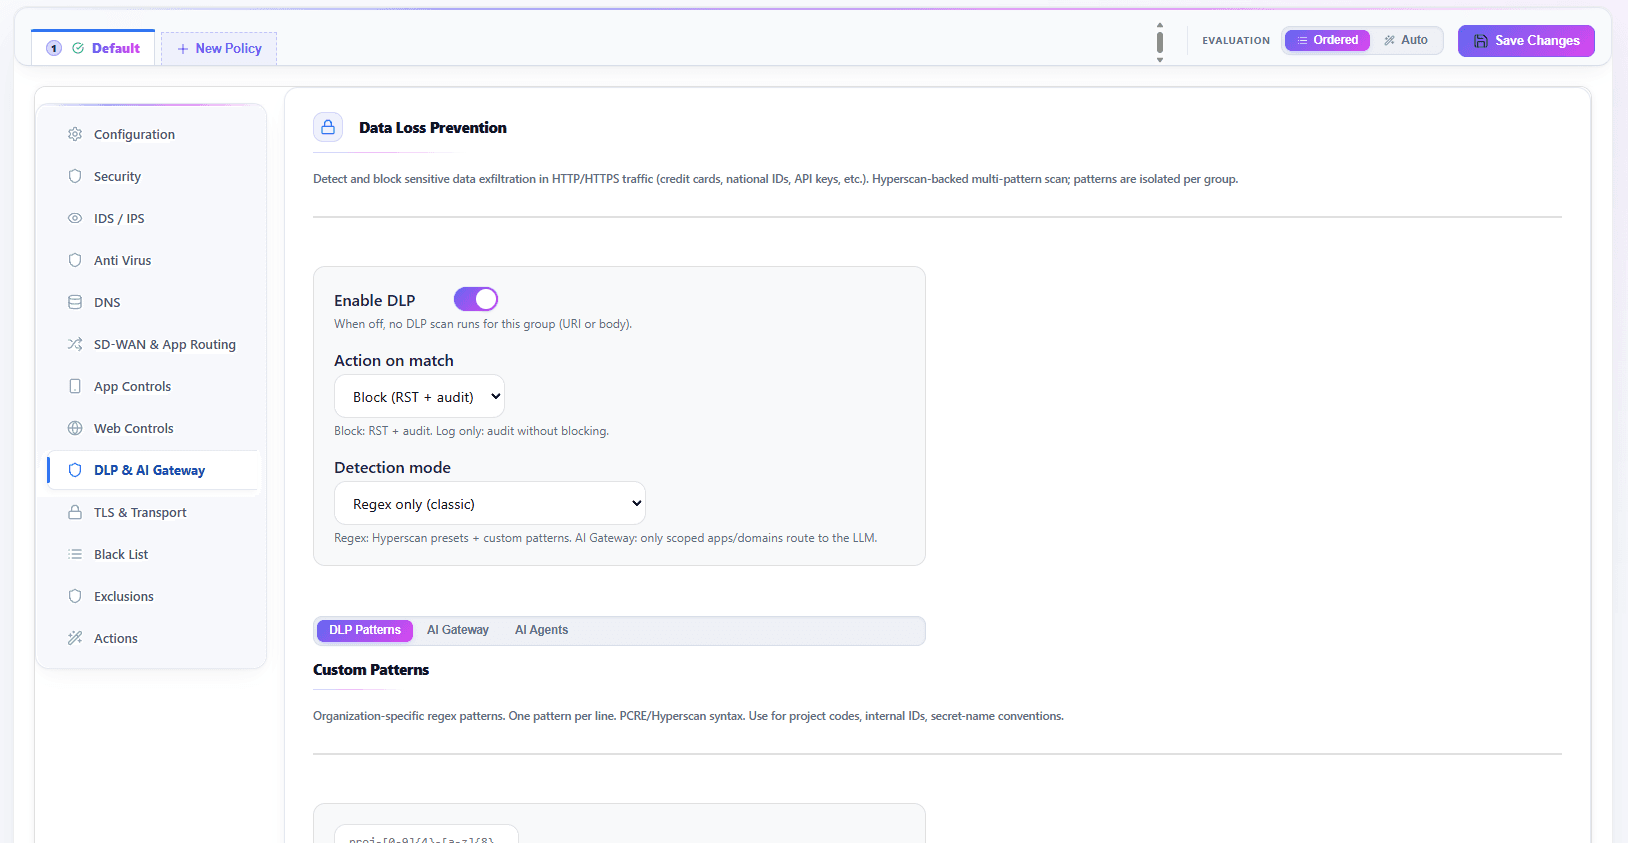
Deterministic matchers plus a local model. Sending content away to ask whether it may be sent is a contradiction.
Watch and record; strip the sensitive part and redirect; or block outright. The rule's action verb is the only change.
ChatGPT, Claude, Gemini, Copilot, Perplexity, Mistral — and an in-house endpoint you declare yourself.
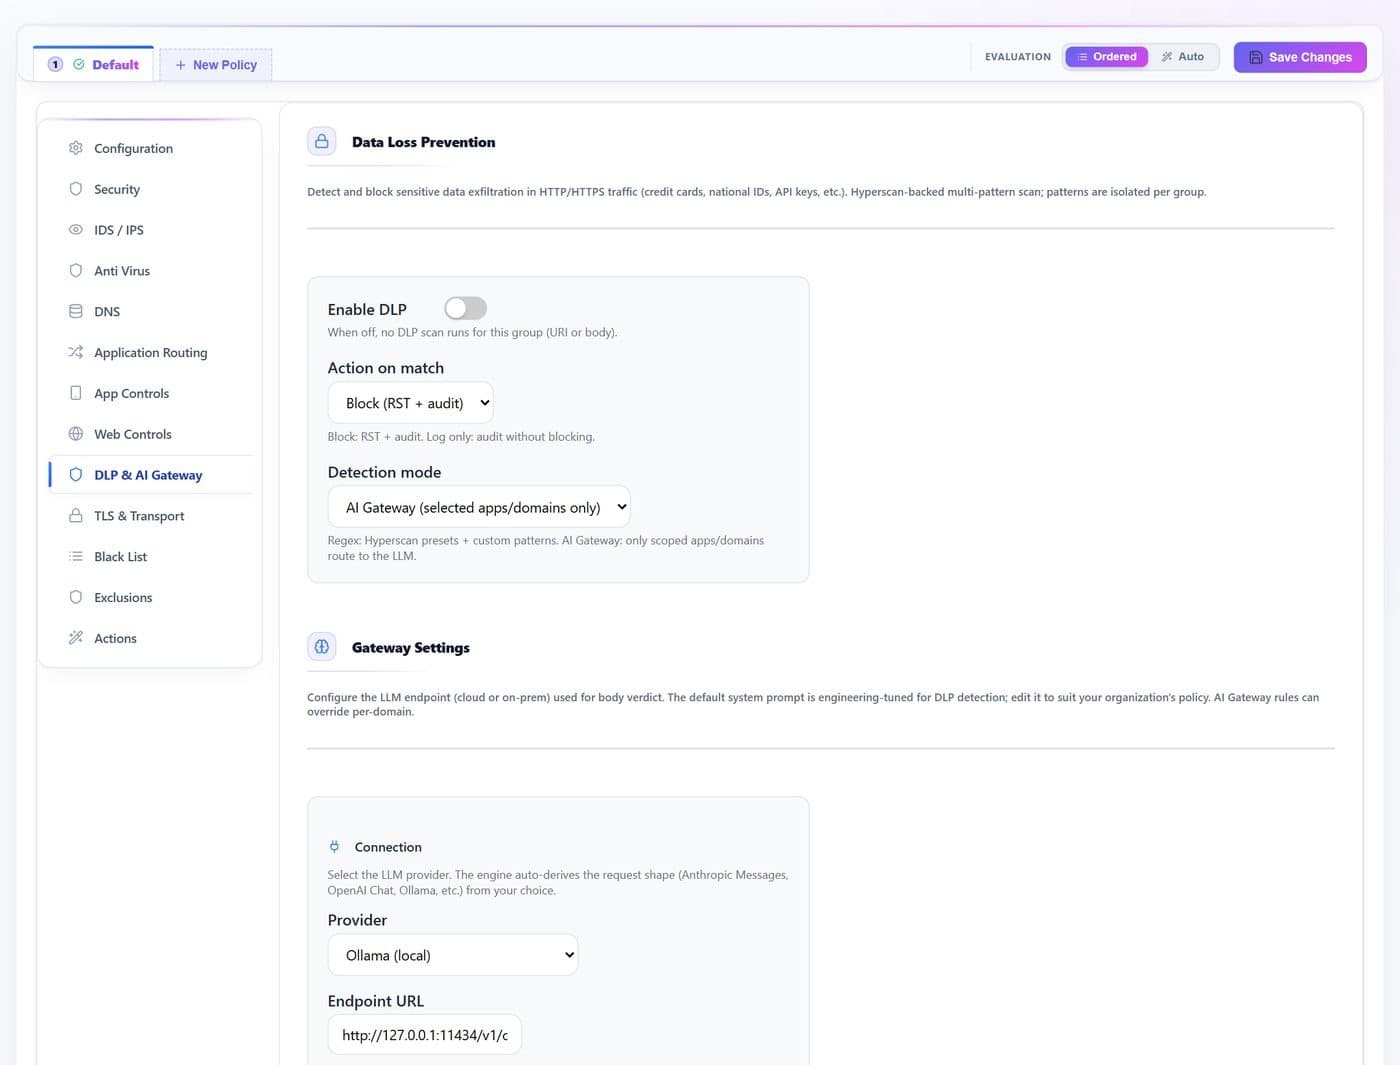
Browser, SDK or script, autonomous agent, MCP client, or none of these — every request is placed in a class before an action is chosen.
The user agent, the shape of the request envelope and the address it is posted to — a raw API endpoint and a chat surface are told apart.
A request carrying tool definitions, calls or results is what turns an assistant into something that acts. It can be allowed, recorded or refused on that ground alone.
Programmatic access to a provider nobody approved is its own case, separate from someone opening the same site in a browser.
Marking forwards the request and records it with a reason and a sensitivity class on the AI activity page — so a class can be watched for a week before anyone decides to block it.
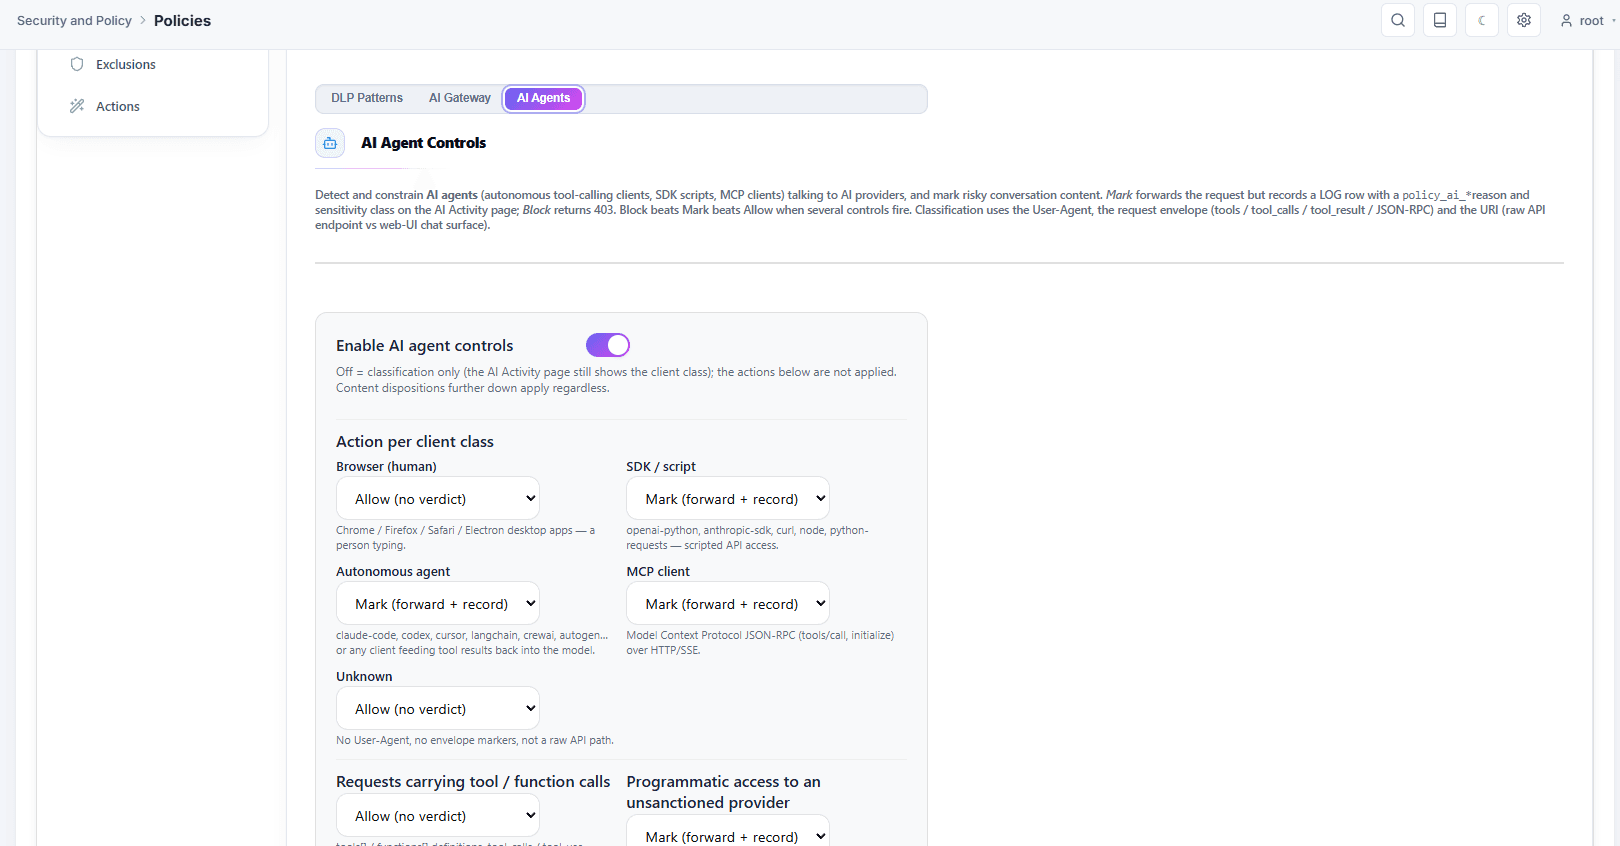
Card numbers, secrets, health and financial data, and national identity formats for twenty-two countries.
A file attached to a web form and a paragraph pasted into a chat are the same risk.
The record names the rule, what was detected and where — without keeping the content itself.
A control that lets traffic past when it cannot evaluate it is not a control on the path that matters.
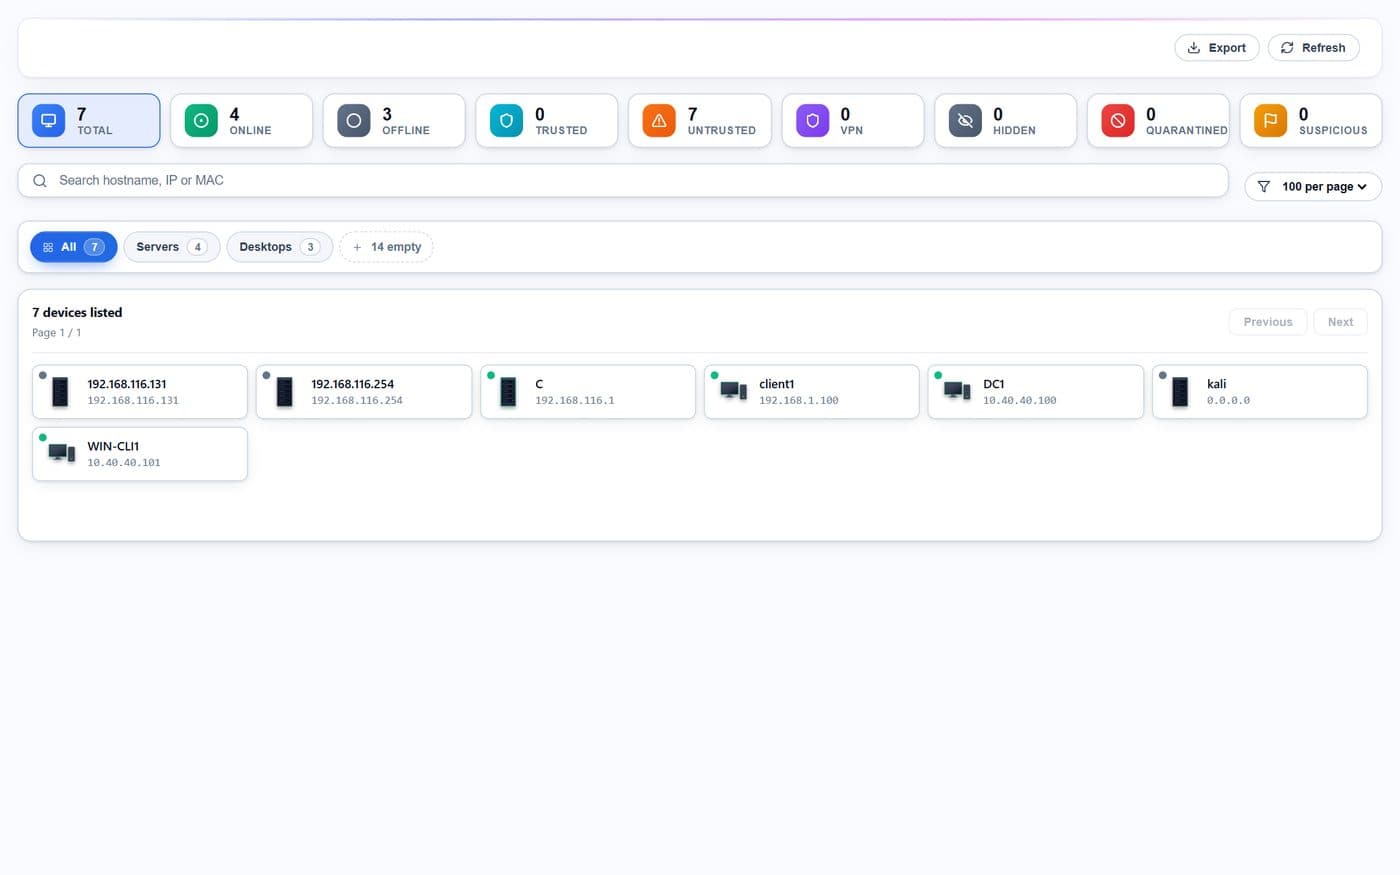
A managed laptop and a personal phone share a subnet and look identical to an address rule. For an enrolled remote device, your own Intune or CrowdStrike says whether it is healthy.
Active Directory, Entra ID or SCIM — and, for a remote person, your own OpenID Connect provider at enrolment. An entitlement follows the person, not their DHCP lease.
A device restricted to what it needs to be fixed is a device you can still fix.
Different rules for a guest network, a server segment, and outside business hours.
Scored on loss, latency and jitter — a link that is up and losing packets is not a healthy link.
WireGuard, OpenVPN or GRE in four shapes — one hub, a hub pair, direct tunnels between spokes, full mesh — provisioned from one topology view rather than hand-built per firewall.
A policy edit takes effect without dropping a packet or interrupting a session.
Reports and live sessions on screen, and CEF, LEEF or syslog over TLS to whatever you run.
Bu sayfaya elle yazılmak yerine paket depolarından alınır; böylece elle yazılmış bir sürüm dizesi gibi kaymaz.
Konsol ve güvenlik duvarı kendi takvimlerinde yayımlanır, bu yüzden numaraları birbirini izlemez. Güvenlik duvarlarınızın her birinin hangi sürümü çalıştırdığı konsolunuzdadır.
Inside OPNsense
Pano · 1 / 6
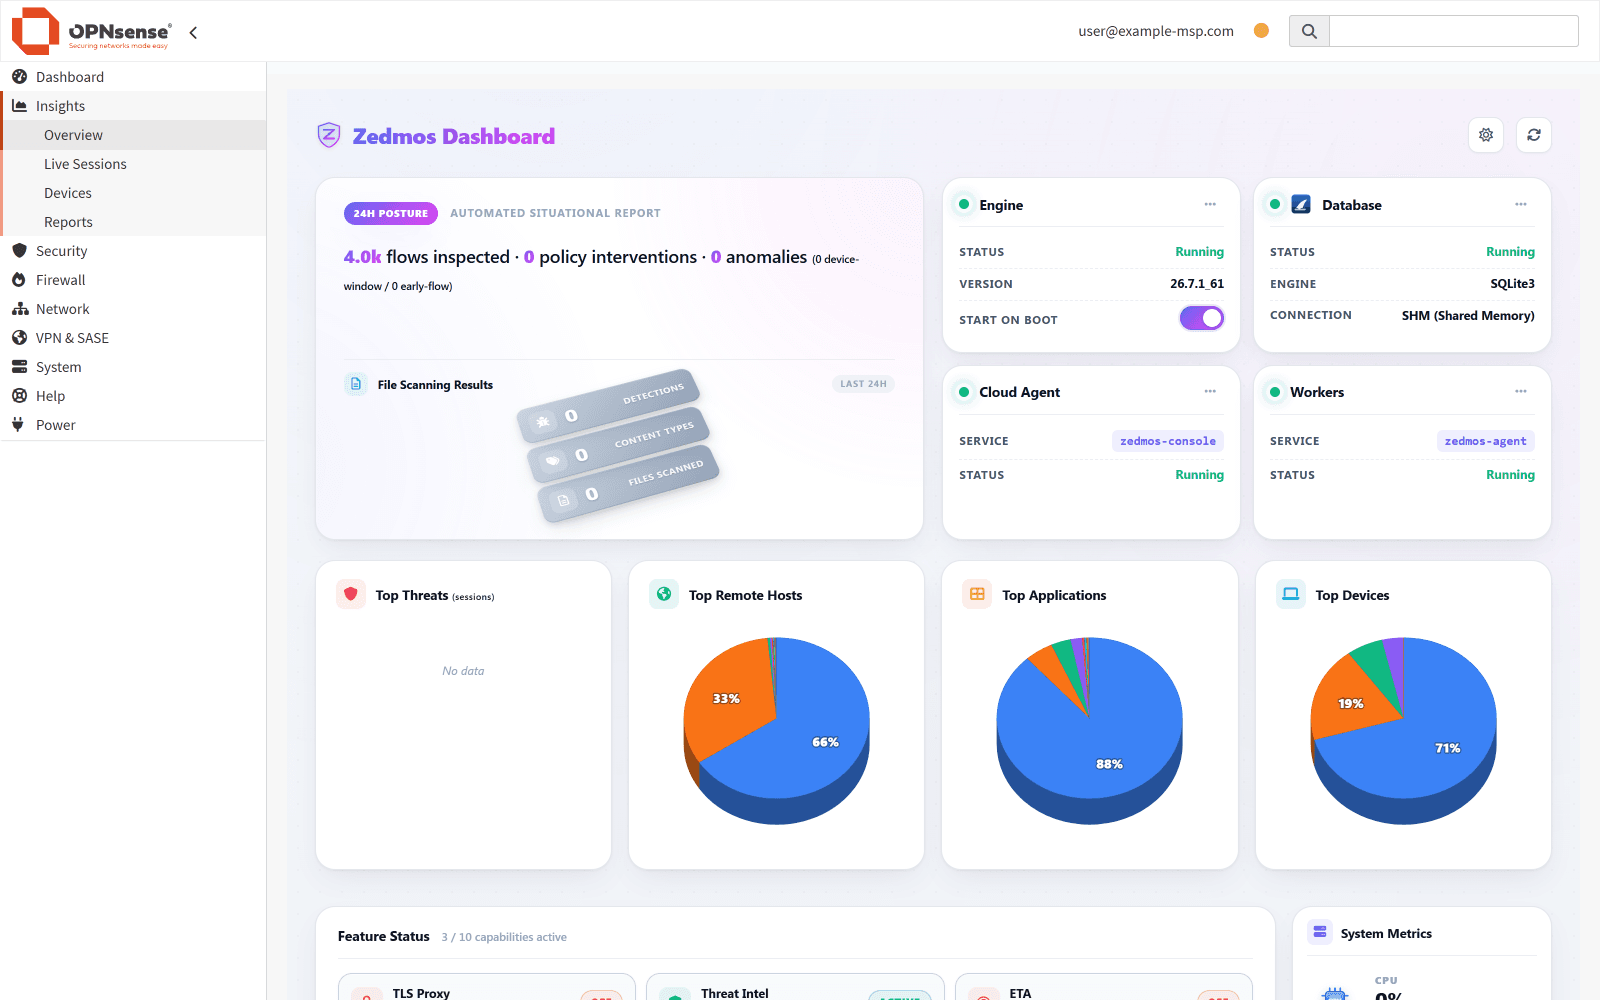
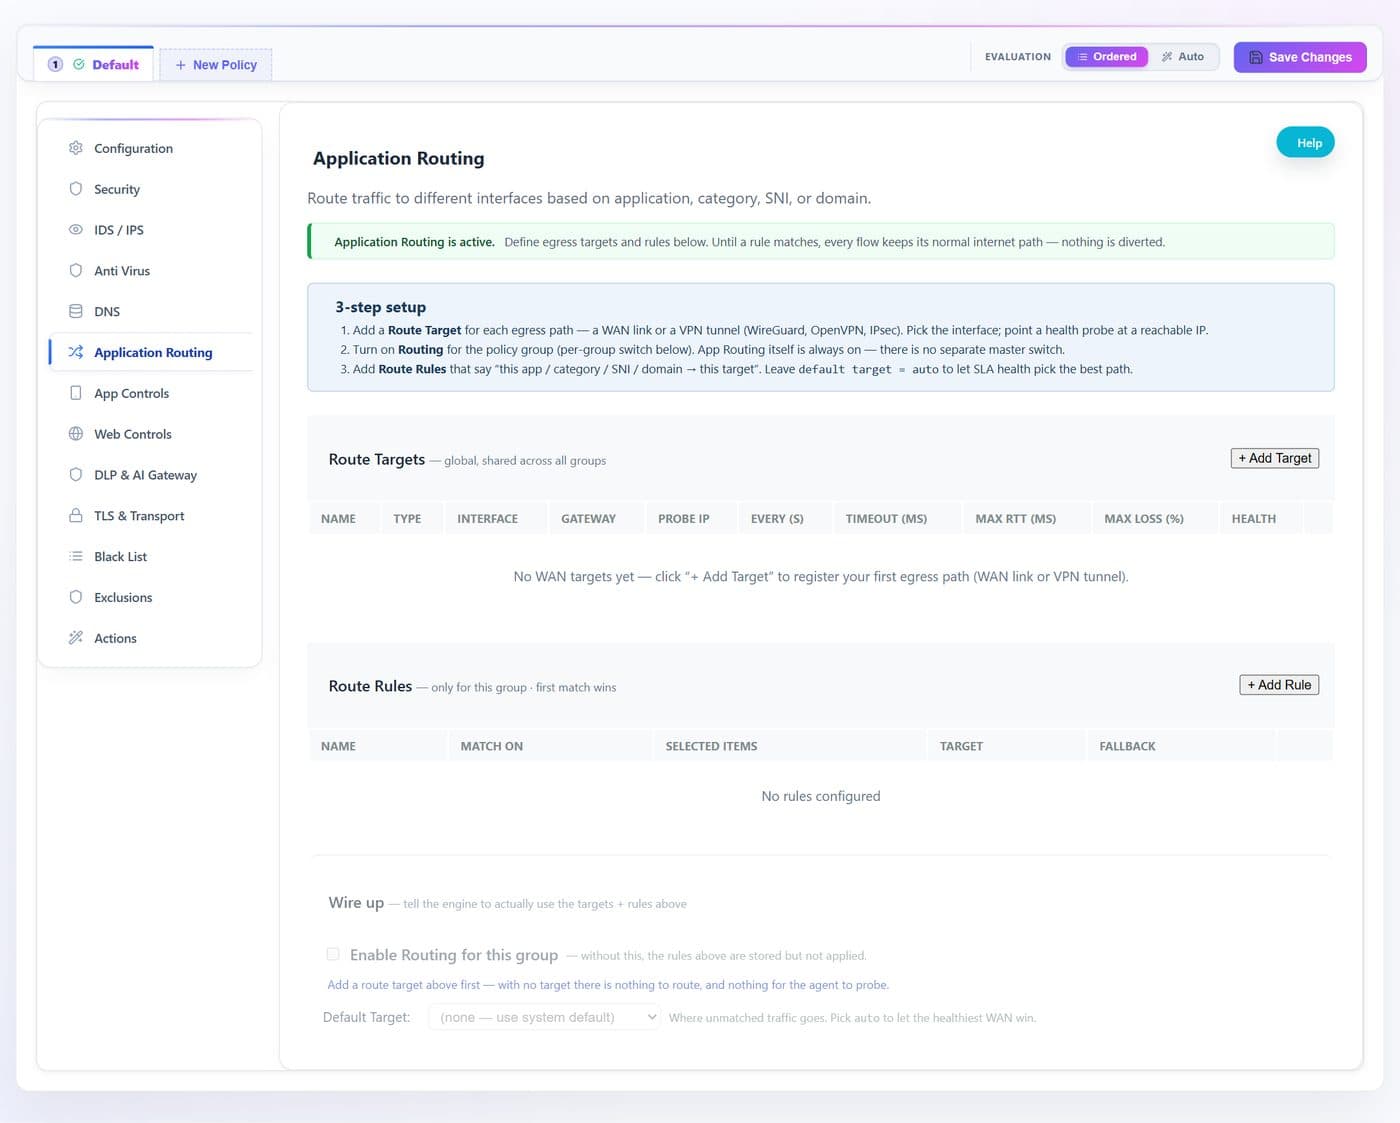
Engine and service health, top threats, applications and devices — rendered inside the OPNsense interface your team already knows.
Mevcut her üretici için bir sayfa; o üreticinin kendi belgelerinden ve kamuya açık kayıtlarından kurulmuş — lisanslama, yaşam döngüsü, yönetim, yargı yetkisi ve istismar geçmişi; her satır kaynağıyla.
Bu sayfa savı ortaya koyar. Şunlar, bunun ekran ekran ve ayar ayar nasıl yapıldığını söyler.
Derin inceleme ve uygulama denetimi, saldırı tespiti ve önleme, TLS incelemesi, veri sızıntısı önleme, bir yapay zekâ ağ geçidi, bağlantılar arasında uygulama başına yönlendirme ve merkezî yönetim; Servisler menüsü altında dokuz sayfa olarak: pano, cihazlar, canlı oturumlar, raporlar, politikalar, ayarlar, bildirimler, güncelleme ve destek.
Platformun kendi paket yöneticisiyle, bir paket deposundan. Kurulumdan sonra Servisler altında görünür ve ayarlar sayfasından kaldırılır.
Hayır. Mevcut kurallar, arayüzler, NAT ve VPN'ler dokunulmadan kalır. Zedmos, onların yerini almak yerine üzerlerine inceleme ve politika ekler.
Zedmos, OPNsense için aynı ürün kategorisinde bir uygulama incelemesi ve IDS/IPS katmanıdır. Onu ayıran: tek kural tabanıyla tek motorda saldırı önleme ve uygulama incelemesi, kendiniz barındırabileceğiniz bir yönetim konsolu, lisansta donanım olmadan güvenlik duvarı başına lisanslama ve aynı motorun ZedmOS üzerinde eksiksiz bir güvenlik duvarı olarak da bulunması.
Evet. OPNsense, pfSense CE ve Zedmos NGFW genelinde tek motor, tek politika modeli ve tek konsol. Karma bir filo bir kez öğrenilir ve aynı biçimde işletilir.
Demo ve fiyatlandırma: info@zedmos.com
Demo talep edin